| English | 释义 | 拼音 |
|---|---|---|
| public key/ˈpʌblɪk kiː/ | 公钥 | gōng yào |
| private key/ˈpraɪvət kiː/ | 私钥 | sī yào |
| antivirus/ˌæntɪˈvaɪrəs/ | 杀毒软件 | shā dú ruǎn jiàn |
| backup/ˈbækʌp/ | 备份 | bèi fèn |
| encryption/enˈkrɪpʃn/ | 加密 | jiā mì |
| firewall/ˈfaɪəwɔːl/ | 防火墙 | fáng huǒ qiáng |
| user accounts/ˈjuːzə əˈkaʊnts/ | 用户账户 | yòng hù zhàng hù |
| audit logs/ˈɔːdɪt lɒɡz/ | 审计日志 | shěn jì rì zhì |
| anti-spyware/ˈænti ˈspaɪweə/ | 反间谍软件 | fǎn jiàn dié ruǎn jiàn |
| access rights/ˈækses raɪts/ | 访问权限 | fǎng wèn quán xiàn |
| authentication/ɔːˌθentɪˈkeɪʃn/ | 身份验证 | shēn fèn yàn zhèng |
| biometrics/ˌbaɪəʊˈmetrɪks/ | 生物识别 | shēng wù shí bié |
| two-factor authentication/tuː ˈfæktə ɔːˌθentɪˈkeɪʃn/ | 双因素认证 | shuāng yīn sù rèn zhèng |
| authorisation/ˌɔːθəraɪˈzeɪʃn/ | 授权 | shòu quán |
| VPN/ˌviː piː ˈen/ | 虚拟专用网 | xū nǐ zhuān yòng wǎng |
| ciphertext/ˈsaɪfətekst/ | 密文 | mì wén |
| least-privilege/liːst ˈprɪvɪlɪdʒ/ | 最小权限 | zuì xiǎo quán xiàn |
| plaintext/ˈpleɪntekst/ | 明文 | míng wén |
| symmetric encryption/sɪˈmetrɪk enˈkrɪpʃn/ | 对称加密 | duì chèn jiā mì |
| asymmetric encryption/ˌeɪsɪˈmetrɪk enˈkrɪpʃn/ | 非对称加密 | fēi duì chèn jiā mì |
| digital signature/ˈdɪdʒɪtl ˈsɪɡnɪtʃə/ | 数字签名 | shù zì qiān míng |
任何人都能锁上、只有一个人能打开的锁
- 每次在线付款,你的卡号都会经过几十台属于陌生人的路由器。其中任何一台都可以复制这些字节。
- 让它安全的是 1977 年的一个想法:一把任何人都能扣上、却只有某一把特定钥匙的持有者能打开的锁。你用商店的公钥锁住卡号;只有商店的私钥能打开它。
- 这只是众多措施中的一种。这一课讲防御——从一台 PC 到开放的互联网——每种措施用考官给分的措辞怎样工作,以及哪种措施对应哪种威胁。
独立的 PC
- 强密码:长、字符混合、定期更换、从不共享。
- 保持更新的杀毒软件(antivirus),及时的软件更新,离开时锁屏。
- 到独立介质的备份(backup),异地保存,让丢失或损坏的数据可以恢复;全盘加密(encryption),让被盗的笔记本什么也交不出。
Which measures protect a standalone PC that is never networked? Select 所有 that apply.
难度 2/5 · 今日首次完成可获 140 金币及少量额外奖励
Malware still arrives on USB sticks and downloads, and disks still fail, so password, antivirus and backups apply. Network log-in auditing is a networked-PC measure.
联网的 PC
- 以上全部,再加防火墙(firewall):它检查每一次进出的传输,与设定的标准比较——例如地址、端口和协议的白名单或黑名单——阻止任何不合标准的传输,并能对未授权访问尝试发出警告。
- 集中管理的用户账户(user accounts),按用户设权限:管理员权限只给管理员。
- 审计日志(audit logs)记录谁登录了、动过什么。
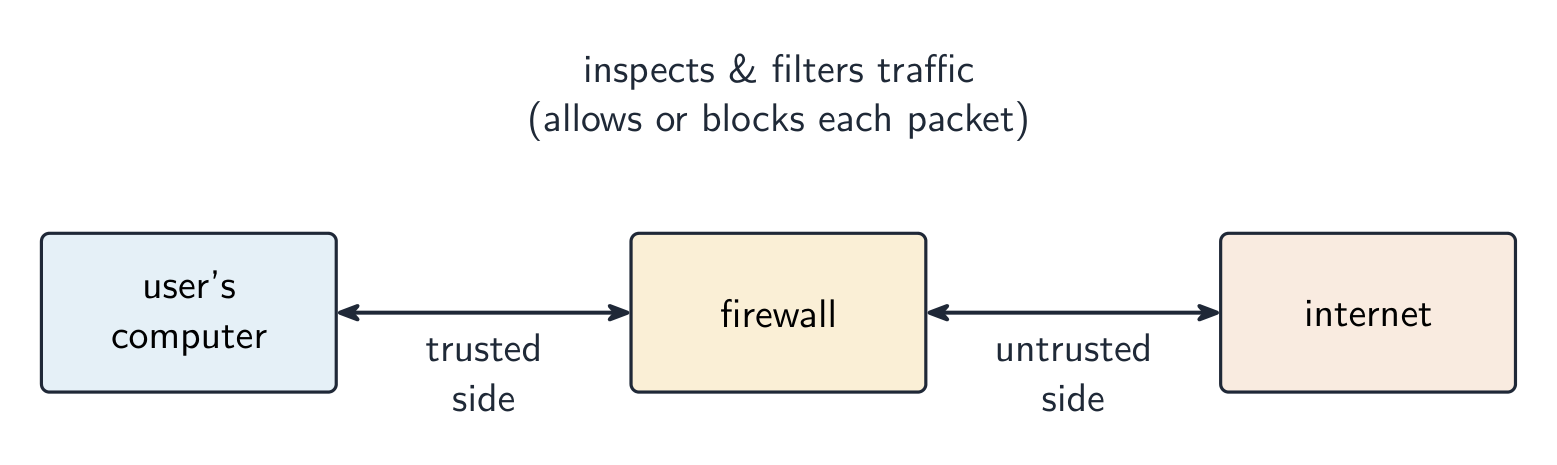
不合标准的流量永远到不了计算机
A firewall mainly:
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
A firewall controls which network traffic is allowed in or out, by a set of rules.
措施怎样工作,用考官的话说
- 杀毒和反间谍软件(anti-spyware)把文件和程序与已知恶意软件特征库比对,检查行为,隔离或删除发现的东西,并且必须更新才能识别新的恶意软件。
- 密码和用户账户:只有知道密码的用户能登录;多次失败后账户锁定;每个账户带有自己的访问权限。
- 访问权限(access rights):每个用户或用户组对每个文件或表获得权限——只读、读写等——所以没有人能看到或更改不属于自己的数据。
- 备份:独立介质上的副本,异地保存,丢失的数据从中恢复。
身份验证
- 身份验证(authentication)核实用户是谁:他们知道的东西(密码)、拥有的东西(令牌或手机),或他们本身的特征(生物识别,biometrics)。
- 生物识别:设备采集面部、指纹或虹膜,转换为数字数据,与该用户存储的数据比对,只在匹配时允许访问。它不会被忘记、借出或猜到。
- 双因素认证(two-factor authentication)组合两个因素,所以单独一个被盗的密码不够用。授权(authorisation)随后决定通过验证的用户可以做什么。
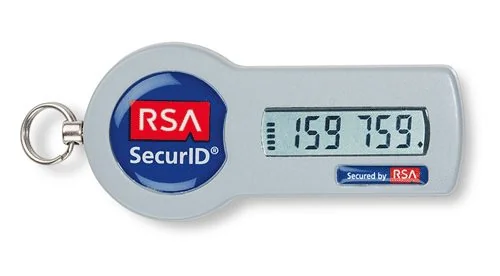
你拥有的东西
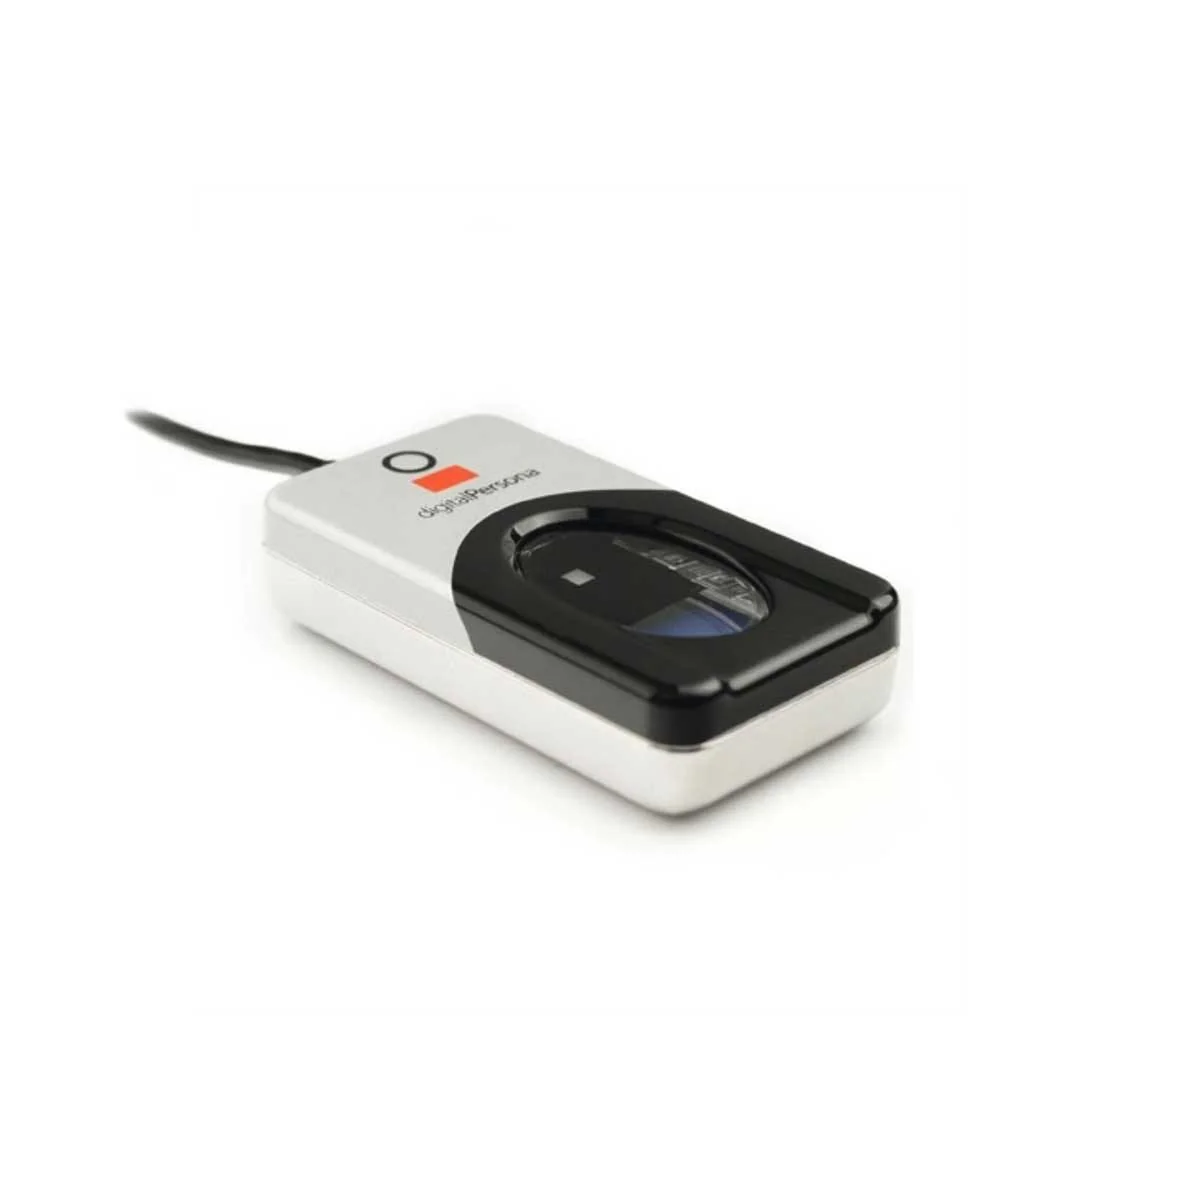
你本身的特征
A code from a phone app is an example of which authentication factor?
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
A token/phone code is "something you have". Two-factor combines it with a password ("know") or biometric ("are").
A fingerprint reader authenticates a user by something they ____.
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
Know (password), have (token), are (biometric feature). A biometric cannot be forgotten, lent or guessed.
把措施与威胁配对
- 传输中被截获:加密数据(HTTPS、虚拟专用网 VPN)。截获的密文没有密钥就毫无用处。
- 未授权访问:强身份验证和双因素,登录失败后锁定。内部滥用:最小权限(least-privilege)原则——每个用户只得到所需的——加上审计。
- 恶意软件:带实时扫描的杀毒和反间谍软件,以及打补丁。网络钓鱼:用户培训、邮件过滤、核对网址。DDoS:限速和流量过滤。
Match each threat to the security measure that best counters it.
难度 2/5 · 今日首次完成可获 140 金币及少量额外奖励
Each threat has a best-fit defence — encrypt against interception, authenticate against intruders, patch against malware, limit privilege against insiders.
The best defence against data being intercepted in transit is to:
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
Encrypted data intercepted in transit is useless without the key. Authentication and antivirus address different threats.
加密
- 加密用密钥把明文(plaintext)打乱成密文(ciphertext),所以截获的副本没有密钥就无法理解;接收者用密钥解密。它保护传输中和存储中的数据。
- 对称加密(symmetric encryption,AES)用同一个共享密钥加密和解密:快,但密钥本身必须安全地到达接收者。
- 非对称加密(asymmetric encryption,RSA)用公钥(public key)加密,用配对的私钥(private key)解密。公钥可以给任何人,这解决了密钥共享问题。
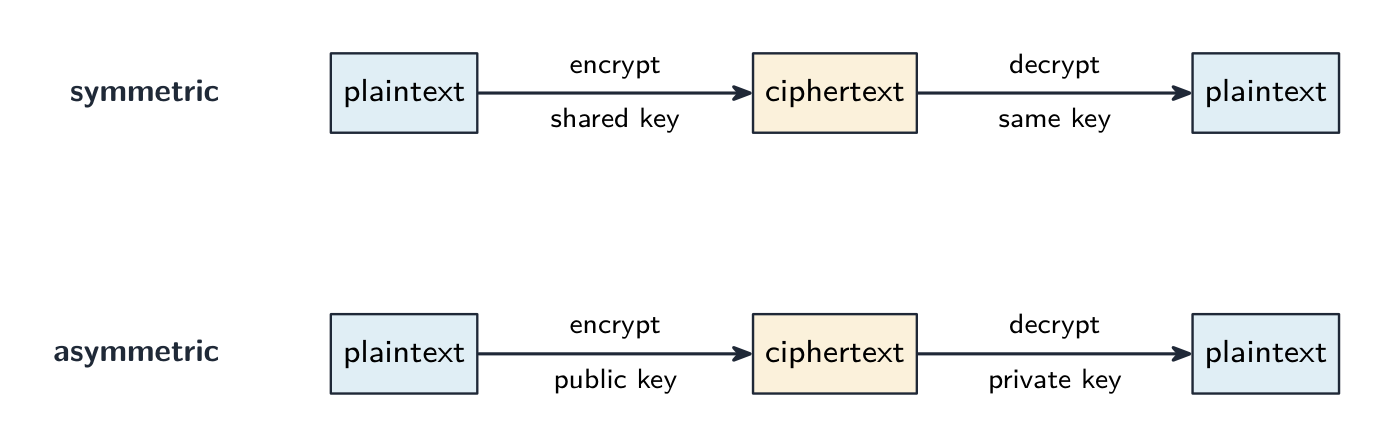
一个共享密钥,或用公钥锁、私钥开
Encrypt with a Caesar cipher
Change the shift — that is the key. Each letter slides that many places along the alphabet to make the ciphertext, and the same key slides it back. That shared key is symmetric encryption in miniature.
Asymmetric encryption (e.g. RSA) differs from symmetric (e.g. AES) because it:
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
Asymmetric uses a public/private key pair (solving key sharing); symmetric uses one shared key (fast).
Put symmetric encryption in order, from sender to receiver.
难度 3/5 · 今日首次完成可获 200 金币及少量额外奖励
Symmetric encryption uses one shared key both to lock (encrypt) and unlock (decrypt) — anyone intercepting the ciphertext can't read it without that key.
Symmetric encryption uses one shared key, while asymmetric encryption uses a public key to encrypt and a private key to decrypt.
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
That public/private split is what lets asymmetric encryption solve the problem of sharing a key safely.
例题:数字签名怎样认证一份文档
- 解释数字签名怎样用于认证一份文档。[5]
- 发送者把消息通过哈希函数得到摘要。发送者用自己的私钥加密摘要;这个加密后的摘要就是数字签名(digital signature)。
- 消息和签名一起发送。接收者用发送者的公钥解密签名,恢复出摘要。
- 接收者对收到的消息做哈希,比较两个摘要。匹配就证明了是谁发的(只有那把私钥能做出这个签名),以及消息未被篡改(任何改动都会改变哈希)。
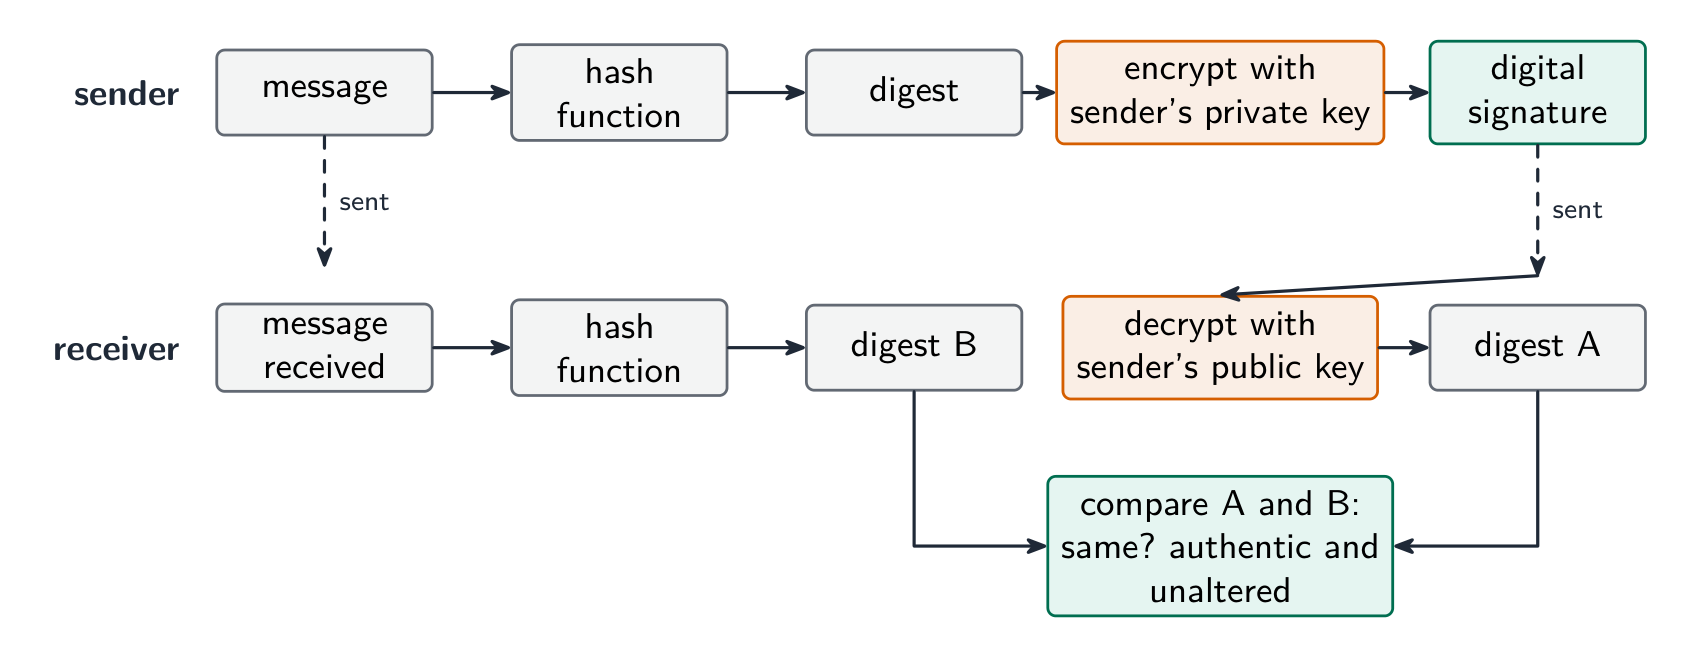
签的是哈希,不是消息
Put the steps of sending and checking a digital signature in order.
难度 3/5 · 今日首次完成可获 200 金币及少量额外奖励
Hash, sign with the private key, send, unlock with the public key, compare. A match proves the sender and that nothing changed.
例题:保密数据穿越互联网
- 一家公司通过互联网向分公司发送保密数据。描述一种保证其安全的方法。[3]
- 加密:数据用密钥编码成密文,所以截获它的未授权者无法读取,只有持有密钥的预期接收者能解码。
- 同样的答案适用于通过邮件发给测试者的程序文件:加密文件,或通过加密连接发送,密码另行发送。
- 说清加密做什么、不做什么:它阻止数据被读取,而不是阻止被截获或删除。
例题:数据库中的访问权限
- 描述访问权限怎样保护数据库中的数据。[3]
- 每个用户获得一个带用户名和密码的账户。数据库管理员给每个账户分配对每个表的权限:只读、读写,或不可访问。
- 用户只能看到被允许的表和字段,所以顾客打不开员工表,职员能读但不能改价格。DBMS 在每次查询时执行这一点。
With access rights, a clerk can be given permission to read the prices table but not to change it.
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
Permissions are set per account and per table: read-only, read and write, or no access. The DBMS enforces them on every query.
容易丢掉的分
- 加密保护保密性,不保护完整性。完整性要用校验和、奇偶校验或校验位。
- 加密不阻止截获或删除;它阻止截获的副本被读懂。
- 数字签名用私钥加密的是消息的哈希,不是消息本身。
- 既要说出措施也要说它怎样工作。单独一个"防火墙"不得分;"把流量与设定标准比较并阻止不合格的"才得分。
你掌握了
- 分层防御:密码、杀毒、更新、备份、加密 → 加防火墙、用户账户、访问权限、审计日志 → 加 VPN、HTTPS、数字签名
- 身份验证是你知道 / 拥有 / 本身的东西;双因素组合两个;生物识别把采集的特征与存储数据比对
- 措施配威胁:截获 → 加密;未授权访问 → 身份验证;内部 → 最小权限;恶意软件 → 杀毒和打补丁
- 对称 = 一个共享密钥;非对称 = 公钥加密、私钥解密;数字签名是用私钥加密的哈希