| English | 释义 | 拼音 |
|---|---|---|
| route/ruːt/ | 路由 | lù yóu |
| validate input/ˈvælɪdeɪt ˈɪnpʊt/ | 校验输入 | jiào yàn shū rù |
| status/ˈsteɪtəs/ | 状态码 | zhuàng tài mǎ |
| SQL injection/ˌes kjuː ˈel ɪnˈdʒekʃn/ | SQL 注入 | SQL zhù rù |
| parameterised query/ˌpærəˈmetəraɪzd ˈkwɪərɪ/ | 参数化查询 | cān shù huà chá xún |
A search string changes the query
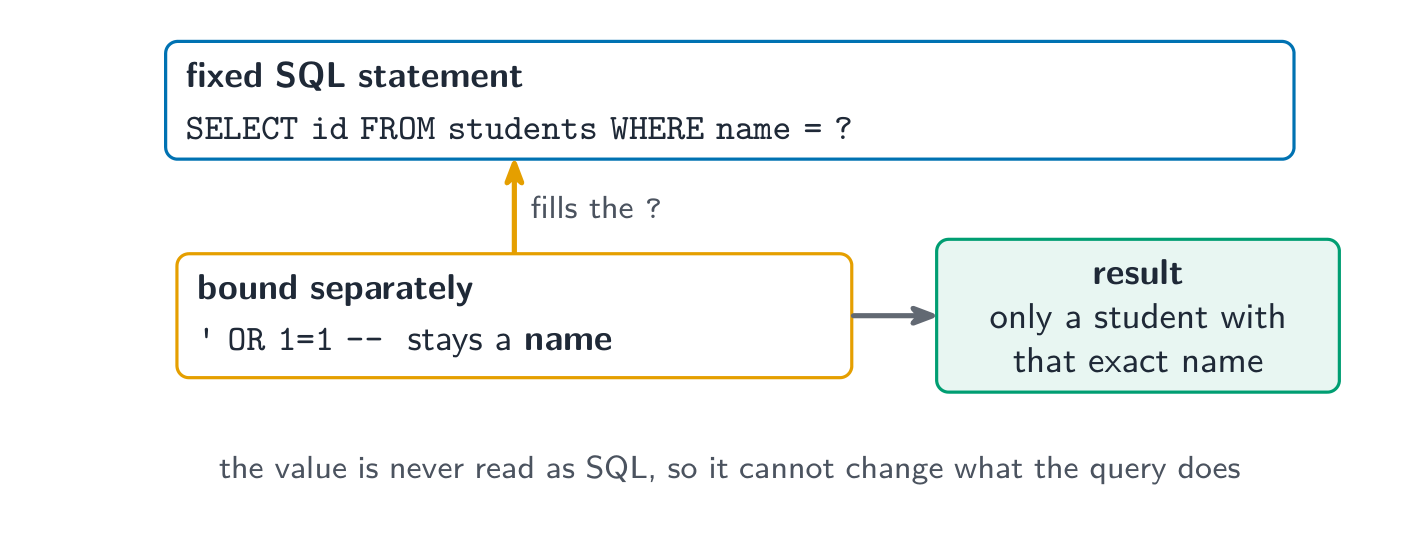
- A name search receives
' OR 1=1 --. If code pastes it into SQL, the text may change the condition instead of remaining a name. - A route 路由 maps a request method and path to its handler. Keep the route contract clear before implementing the lookup.
Check shape and permission
- Validate input 校验输入 means checking required values, types, permitted lengths and ranges. Check the caller’s permission separately.
- A status 状态码 describes the result: 200 for this successful lookup, 400 for invalid input and 404 for a missing resource. Permission failures need the application’s agreed policy; they are not automatically bad input.
根据课程的路线契约对这些结果进行匹配。
难度 2/5 · 今日首次完成可获 140 金币及少量额外奖励
这些含义本身并不能定义私有权限失败应如何表示。
Keep values outside the SQL text
- SQL injection SQL 注入 happens when untrusted text becomes part of SQL syntax. A parameterised query 参数化查询 binds a value separately from the statement.
- Placeholders bind values, not arbitrary table names or sort directions. Choose such identifiers from a fixed server-side allowlist when a route needs them.
哪种查找方式能将提交的名字与 SQL 语法分开?
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
绑定值使其与固定的语句分开。
解释将名称绑定到SQL占位符会发生什么变化。
难度 3/5 · 今日首次完成可获 200 金币及少量额外奖励
语句本身保持不变,而单独绑定的值仍然是数据。
占位符用于绑定值,因此表名和排序方向必须源自固定的服务器端白名单。
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
正确。占位符不能安全地替代标识符;应从服务器端已知安全选项中选取动态标识符。
Run a complete local example
- Save and run this Python example using SQLite. The unusual string is stored as a name, then searched as a bound value.
- The result contains only that named row. Binding prevents this value becoming SQL syntax; it does not establish permission or make every application secure.
import sqlite3

con = sqlite3.connect(":memory:")
con.execute("CREATE TABLE students (id INTEGER PRIMARY KEY, name TEXT)")
name = "' OR 1=1 --"
con.executemany("INSERT INTO students VALUES (?, ?)", [(1, "Mei"), (2, name)])
rows = con.execute("SELECT id FROM students WHERE name = ?", (name,)).fetchall()
print(rows)  # [(2,)]
con.close()
完整的SQLite示例会打印出什么内容?
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
该特殊字符串会被存储,然后作为字面量名称进行匹配。
Keep failures useful and private
- Give the browser a clear message it can act on, such as an invalid field or a temporary failure. Do not return raw SQL errors, private credentials or stack traces.
- Record diagnostic details only in protected logs with sensitive values removed. Log enough context to investigate without copying every private request body.
向普通访客返回原始数据库错误,以便他们调试SQL语句。
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
返回有用的安全提示信息;保护诊断日志并移除敏感值。
Verify more than a happy path
- Check valid, missing, wrong-type and oversized input; denied access; an empty match; and a simulated database failure. State the expected result for each.
- Keep every dynamic value bound, including dropdown values. The browser’s list does not prevent someone sending a different value directly.
Validate the request, authorize the caller and bind data values. These solve different problems; none replaces the others.
哪些外部输入需要进行适当的服务器端检查?请选择所有适用的选项。
难度 2/5 · 今日首次完成可获 140 金币及少量额外奖励
看似普通的输入值仍可能具有错误的类型、长度或权限。
查询已参数化,但任何调用者都能读取私有学生记录。还缺少什么?
难度 1/5 · 今日首次完成可获 100 金币及少量额外奖励
值的注入绑定地址;它并不授权调用者。