Authentication
Введено| English | Значение |
|---|---|
| hash/hæʃ/ | Хэш-значение |
| cryptographic hash function/ˌkrɪptəˈɡræfɪk hæʃ ˈfʌŋkʃn/ | Криптографическая хэш-функция |
| salt/sɒlt/ | соль |
| biometric/ˌbaɪəʊˈmetrɪk/ | биометрические данные |
| password spraying/ˈpæswɜːd ˈspreɪɪŋ/ | распыление паролей |
| credential stuffing/krɪˈdenʃl ˈstʌfɪŋ/ | подмена учётных данных |
Hashing passwords
- A cryptographic hash function 密码散列函数 turns any input into a fixed-length hash 散列值.
- It is one-way: you cannot work backwards to the input.
- The same input always gives the same hash (repeatable).
Salt and storage
- A service stores the hash, never the plaintext password.
- Salt 盐值 (random bits) is added so identical passwords hash differently.
- At login, the system hashes what you typed and compares.
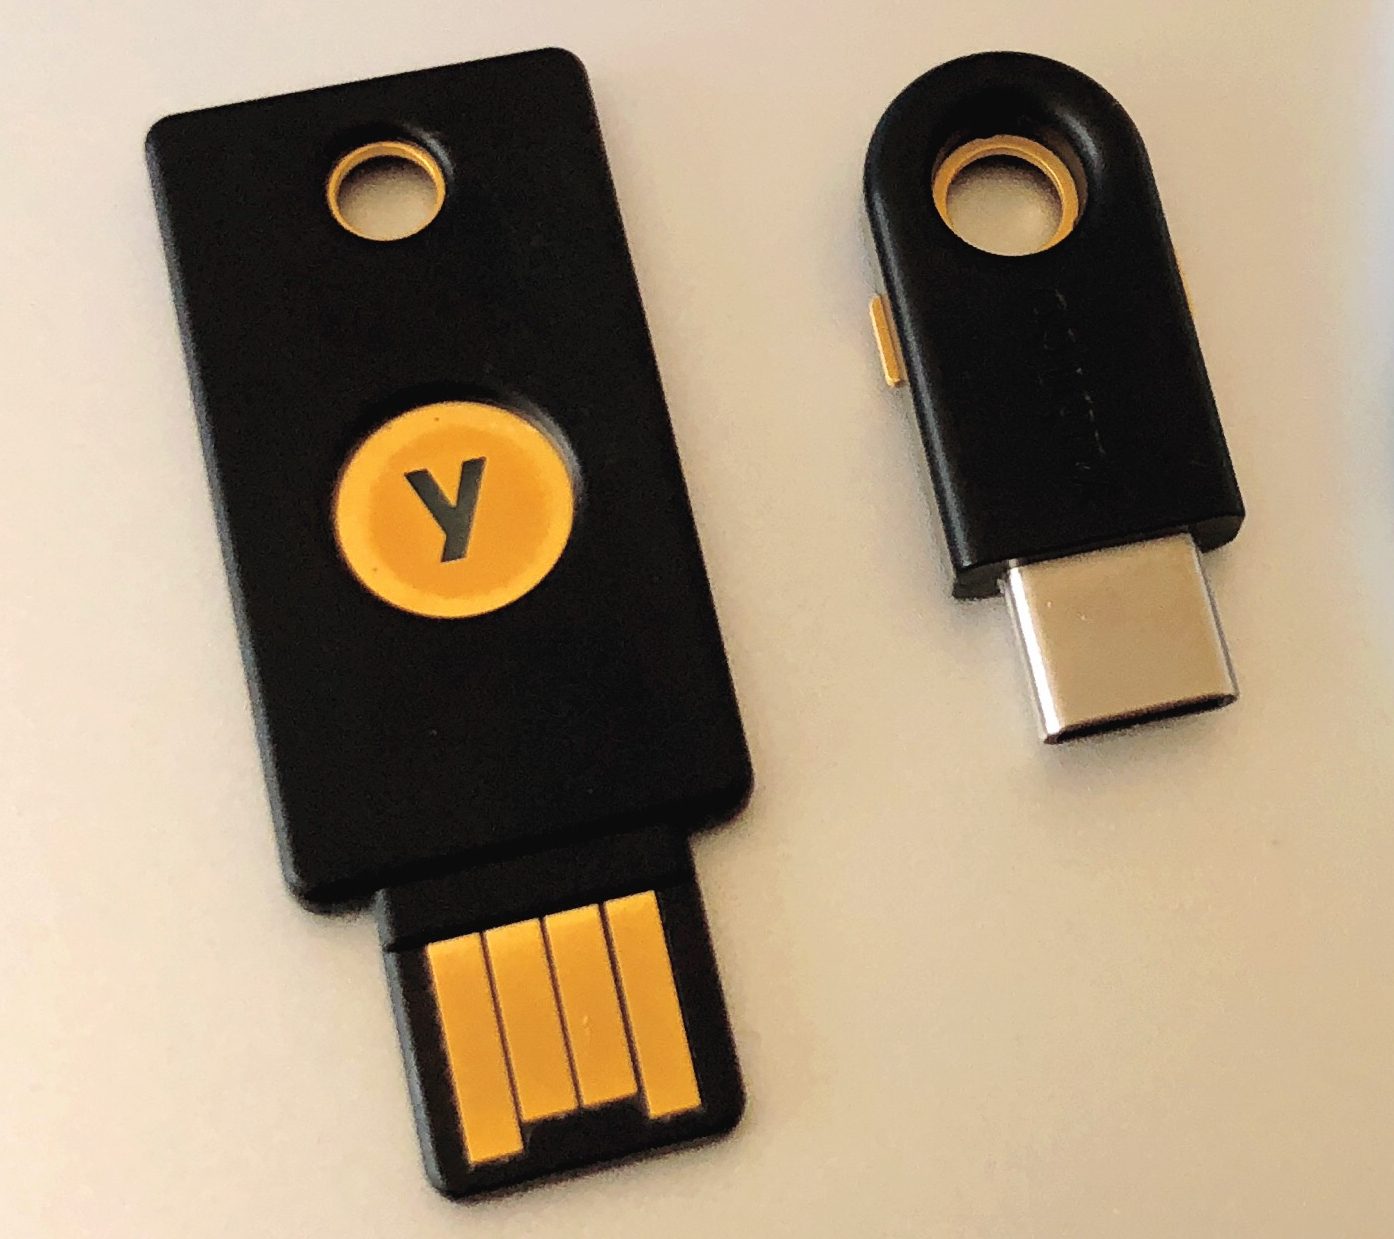
A hardware security key proves who you are with something you physically hold— a strong second factor
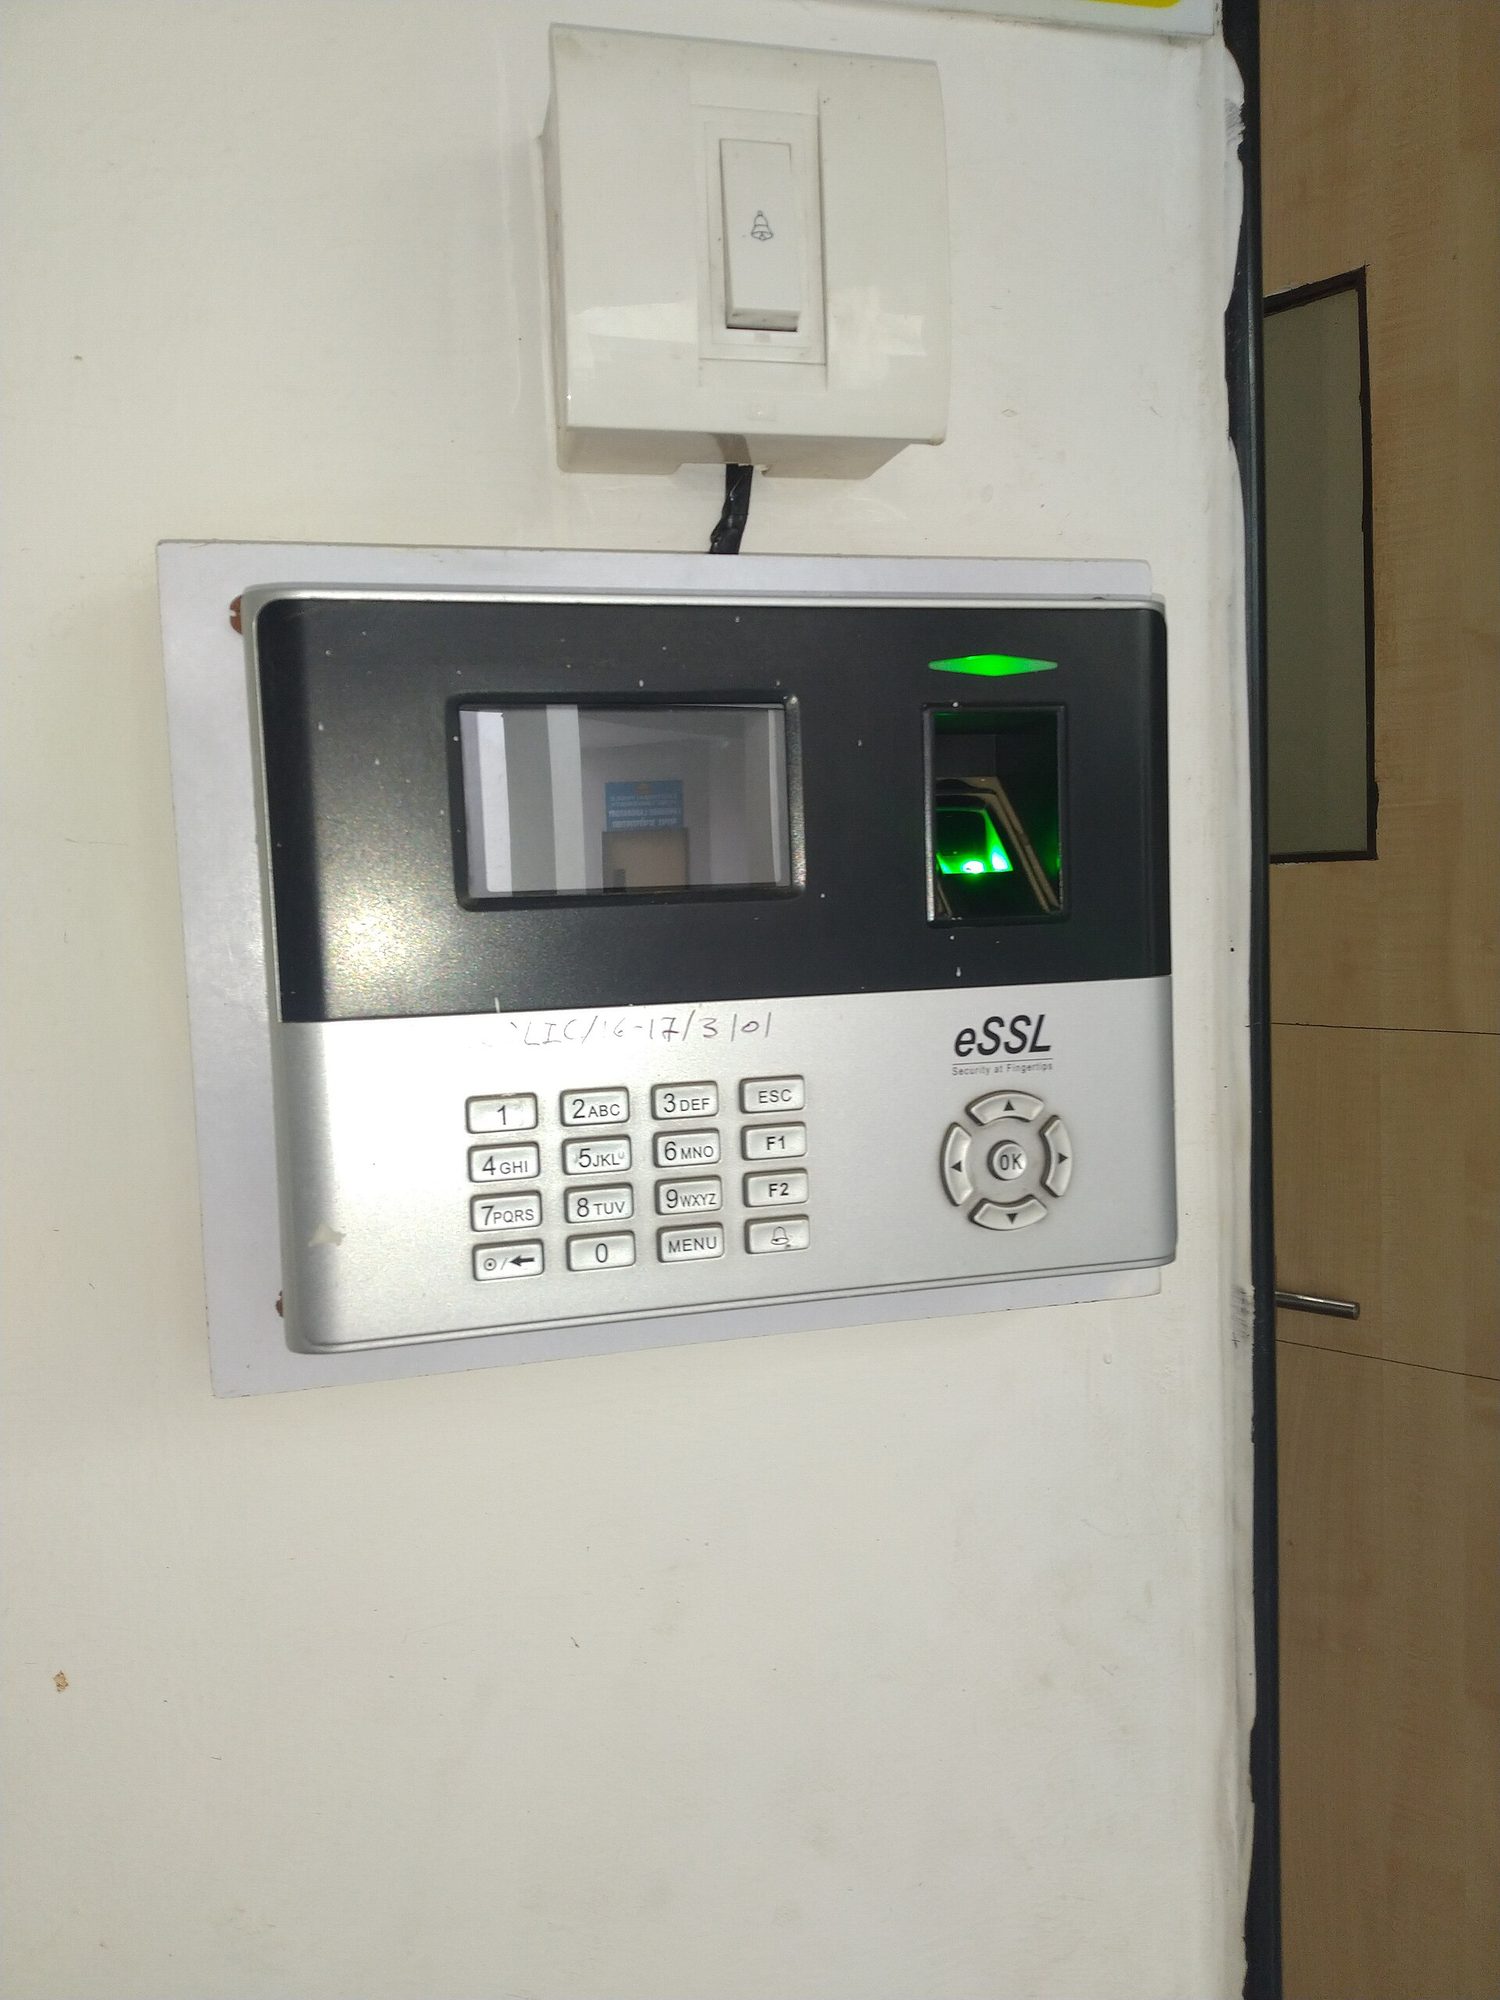
A fingerprint scanner: biometric 生物特征 authentication checks something you ARE, which is much harder for an attacker to steal or guess than a password
Which authentication factor?
Factors are: something you know, something you have, something you are (biometric), somewhere you are.
A cryptographic hash output is...
Сложность 1/5 · 100 монет + небольшой бонус за первое выполнение сегодня
A hash is fixed-length and one-way.
Trying one common password against many accounts is...
Сложность 1/5 · 100 монет + небольшой бонус за первое выполнение сегодня
Password spraying = one password, many users.
Password attacks & factors
- Password spraying 密码喷洒: one common password against many accounts.
- Credential stuffing 撞库: stolen or default credentials.
- Factors: something you know / have / are (biometric) / where — combine for MFA.
A service should never store your plaintext password. If it emails you your actual password when you forget it, it is storing passwords unsafely — a serious red flag. Safe services store only the salted hash.
Salt makes two identical passwords produce the same stored hash.
Сложность 1/5 · 100 монет + небольшой бонус за первое выполнение сегодня
False. A unique salt per user changes each hash, so identical passwords produce different stored hashes and precomputed tables do not work.
Using two or more authentication factors is called ____.
Сложность 1/5 · 100 монет + небольшой бонус за первое выполнение сегодня
MFA combines factors for stronger security.
Match each proof to its factor type.
Сложность 2/5 · 140 монет + небольшой бонус за первое выполнение сегодня
Know / have / are are the classic factor types.
Two users both pick the password sunshine. Without salt, both stored hashes are identical, so cracking one cracks both. With a unique salt each, the two hashes look completely different — the attacker must crack each one separately.
Passwords are stored as a one-way, fixed-length hash, with salt so identical passwords differ. Attacks include spraying (one password, many accounts) and stuffing (stolen/default credentials). Authentication factors — know / have / are / where — combine into MFA.