Detecting Network Attacks
Đã giới thiệu| English | Ý nghĩa |
|---|---|
| NIDS/nɪdz/ | hệ thống phát hiện xâm nhập mạng |
| NIPS/nɪps/ | hệ thống phòng thủ xâm nhập mạng |
| SIEM/siːm/ | quản lý thông tin và sự kiện an ninh |
| signature-based/ˈsɪɡnɪtʃə beɪst/ | dựa trên chữ ký |
| anomaly-based/əˈnɒməli beɪst/ | dựa trên bất thường |
| baseline/ˈbeɪslaɪn/ | đường cơ sở |
Detection systems
- A NIDS 网络入侵检测系统 analyses traffic and raises an alert, but does not block.
- A NIPS 网络入侵防御系统 can also stop an attack.
- A SIEM 安全信息与事件管理 gathers data from many sources to spot patterns.
Two detection methods
- Signature-based 基于特征: matches known attack signatures — fast, few false alarms.
- Anomaly-based 基于异常: compares to a normal baseline 基线 — catches new attacks.
- A hybrid approach combines both.
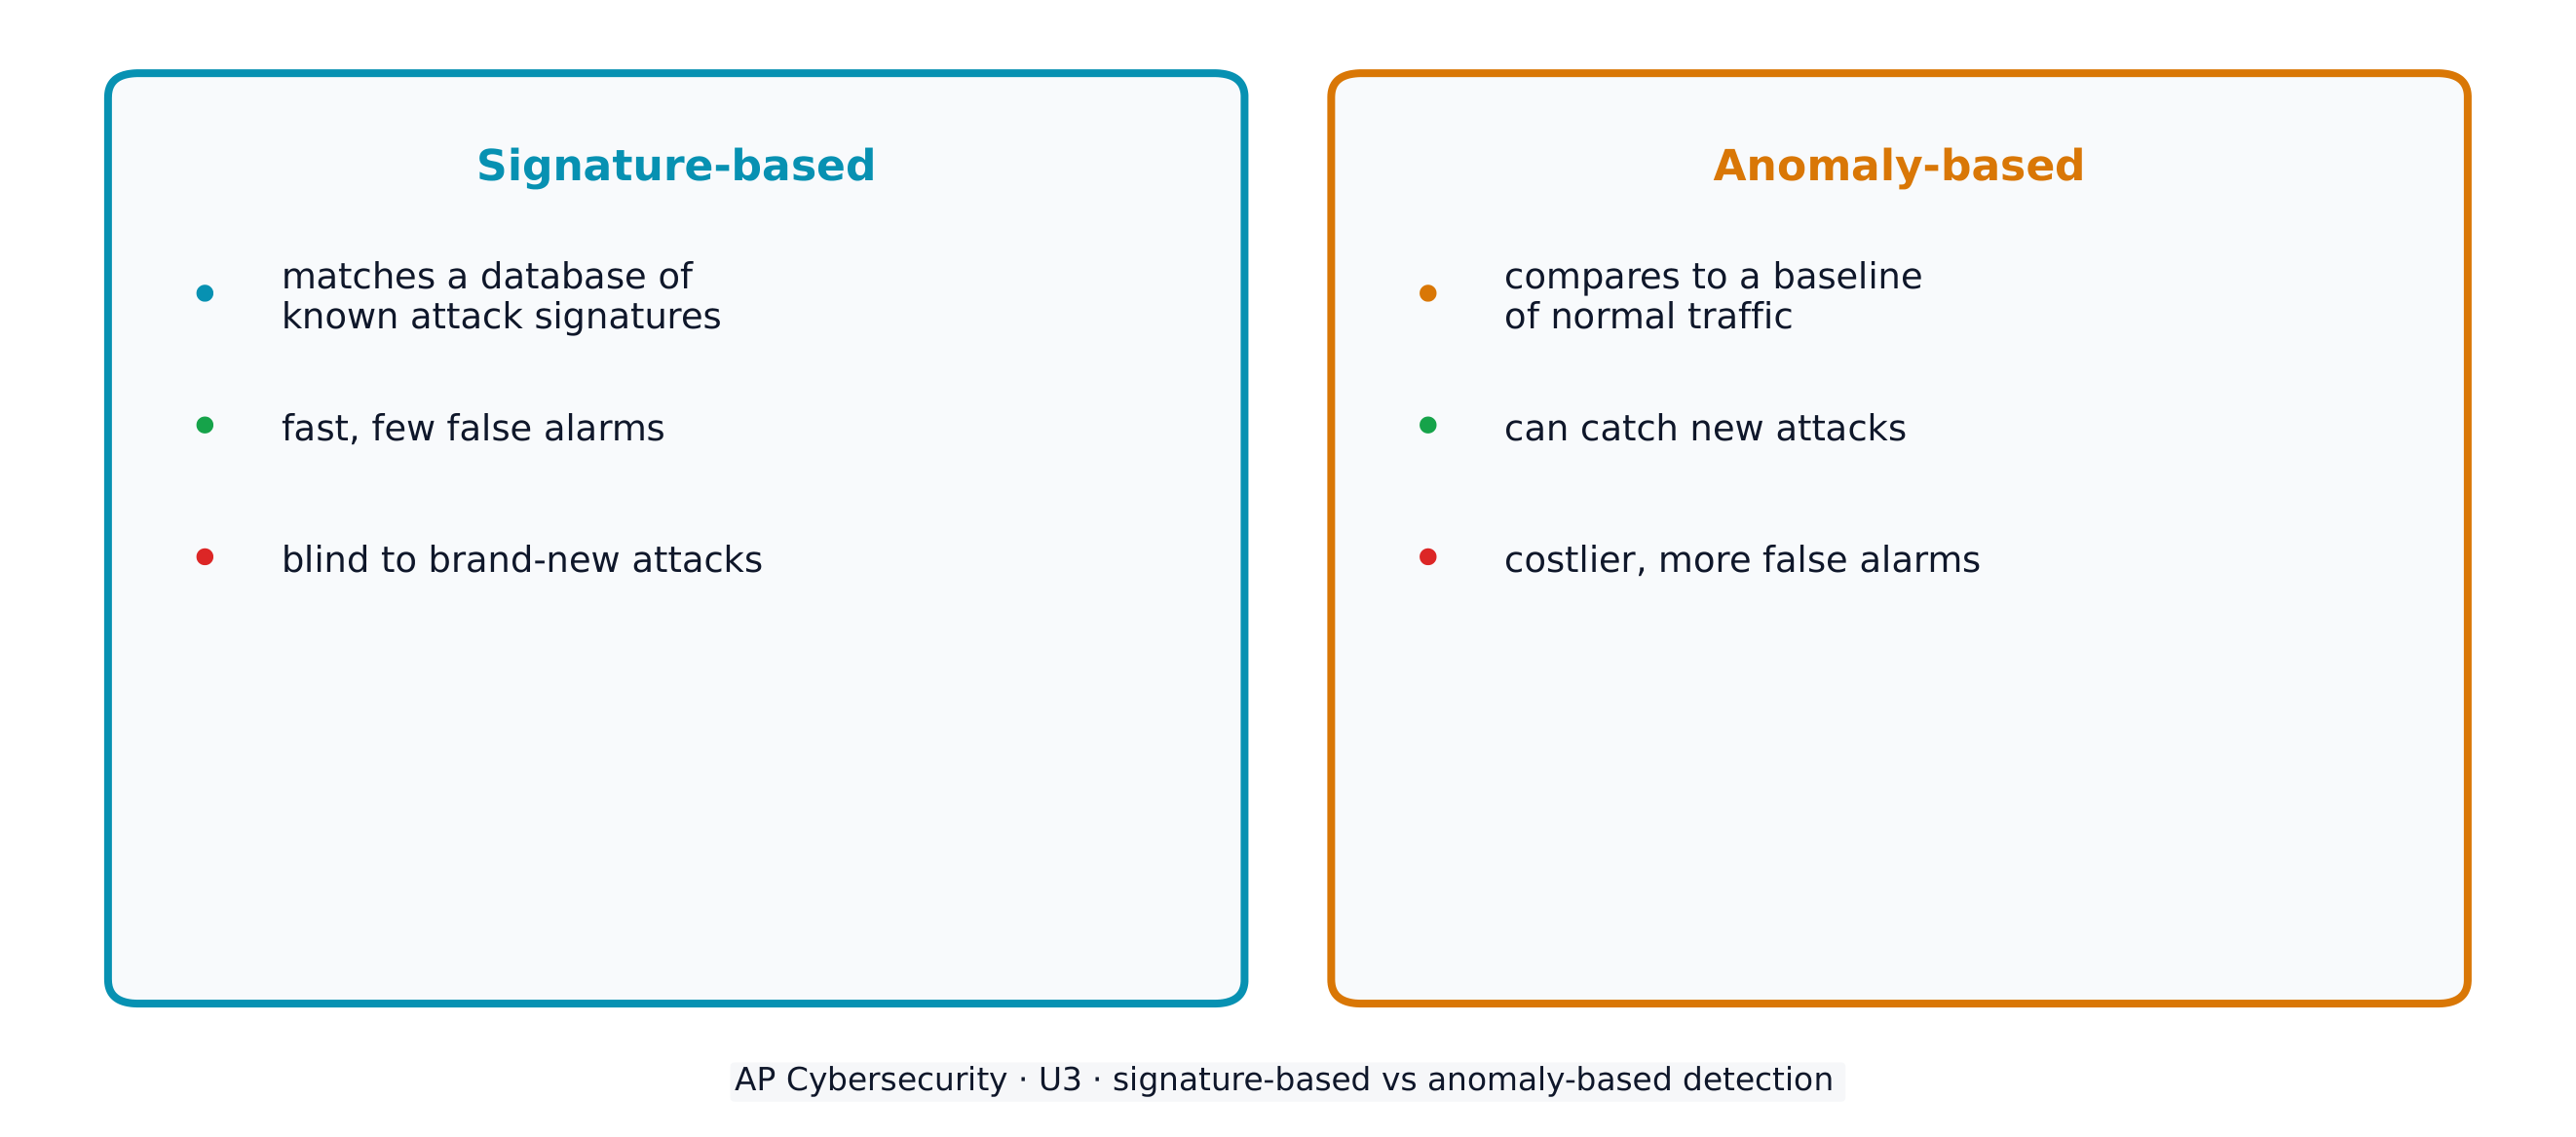
Signature-based detection matches known attacks; anomaly-based detection spots unusual behaviour
Signature-based or anomaly-based detection?
Signature-based matches known attacks (fast, few false alarms); anomaly-based flags deviations from normal (catches new attacks).
Which system detects an attack and raises an alert but does NOT block it?
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
A NIDS alerts only; a NIPS can block.
Which detection method is more likely to catch a brand-new attack?
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
Anomaly-based flags the unusual; signatures miss the new.
Anomaly-based detection compares traffic to a normal ____.
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
It flags deviation from the baseline.
Which describe a SIEM? (Choose all)
Độ khó 2/5 · 140 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
A SIEM is software, not a physical lock.
The trade-off
- Signature-based is blind to brand-new attacks (more false negatives).
- Anomaly-based costs more and raises more false alarms.
- Choose by traffic volume, novelty risk, and budget.
Do not confuse an IDS with an IPS. An intrusion detection system only alerts — a human must act. An intrusion prevention system can block the attack itself. The one letter changes what happens.
Signature-based detection reliably catches brand-new attacks with no known signature.
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
False. Signature-based detection is fast with few false positives, but it misses attacks with no known signature; anomaly-based detection is needed for those.
A new, never-seen worm hits the network. A signature-based system has no signature for it, so it misses it (a false negative). An anomaly-based system notices the unusual traffic pattern and flags it — the classic reason to include anomaly detection.
Detect network attacks with a NIDS (alerts), NIPS (blocks), or SIEM (correlates). Signature-based detection is fast but misses new attacks; anomaly-based catches novel attacks but costs more and raises false alarms. Pick by volume, novelty, and budget.