Protecting Networks: Firewalls
Đã giới thiệu| English | Ý nghĩa |
|---|---|
| firewall/ˈfaɪəwɔːl/ | firewall |
| stateless/ˈsteɪtləs/ | không trạng thái |
| stateful/ˈsteɪtfl/ | có trạng thái |
| access control list/ˈækses kənˈtrəʊl lɪst/ | danh sách kiểm soát truy cập |
What a firewall does
- A firewall 防火墙 allows or denies traffic in or out of a network.
- Stateless 无状态 filters on packet headers alone.
- Stateful 有状态 also tracks each connection's state.
The ACL and first match
- A firewall follows an access control list (ACL) 访问控制列表.
- Rules are checked in order; the first match wins.
- So the order of rules changes which traffic gets through.
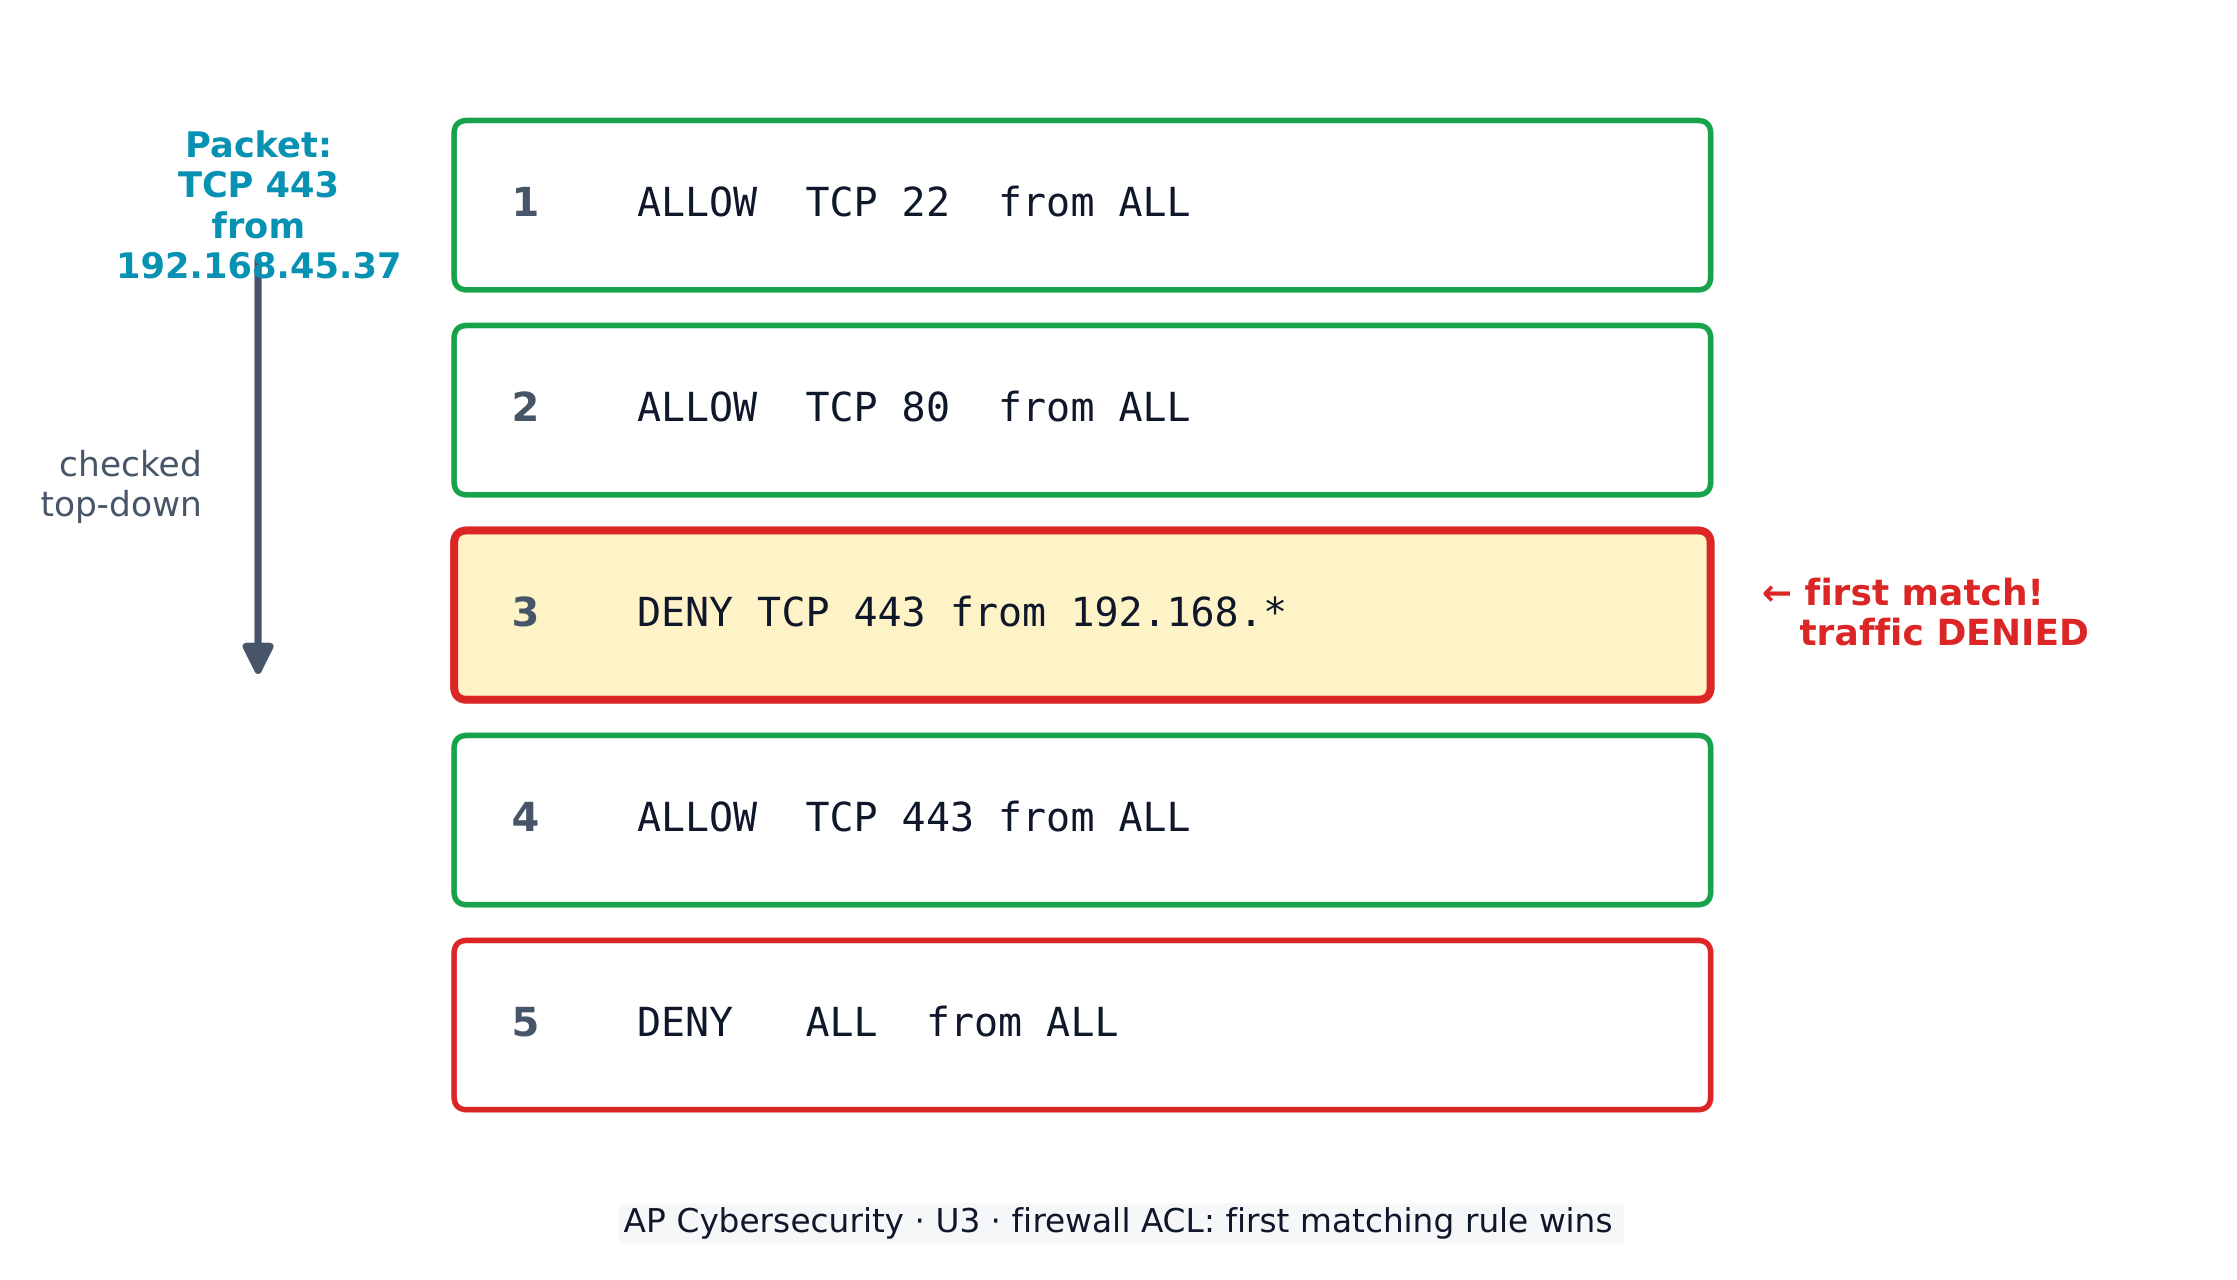
A firewall checks each packet against its rules from the top; the first match wins
Which firewall rule fires first?
A firewall checks its ACL top-to-bottom and applies the first rule that matches the packet.
In a firewall ACL, which rule is applied to a packet?
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
The first matching rule wins.
A firewall that tracks the state of each connection is...
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
Stateful firewalls track connections.
A firewall's ordered set of permit/deny rules is called an ____.
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
The ACL (access control list) drives the firewall.
Where firewalls belong
- At every gateway between the internal network and the internet.
- At the boundary of each network segment.
- Each firewall's security level can be set independently.
Rule order is everything. A Deny rule placed above an Allow rule for the same traffic blocks it — even though the Allow exists lower down. Read an ACL top-to-bottom and stop at the first match.
If an ALLOW rule appears below a DENY rule for the same traffic, the traffic is allowed.
Độ khó 1/5 · 100 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
False. Firewall rules are checked top-down and the first match wins, so the DENY above fires first and the traffic is blocked.
A packet is TCP 443. Order the rules by which is checked first.
Độ khó 3/5 · 200 xu + một phần thưởng nhỏ cho lần hoàn thành đầu tiên trong ngày
Rules are checked top-down; the packet is denied at Rule 2 before reaching Rule 3.
Rule 1: ALLOW TCP 22; Rule 2: DENY TCP 22. SSH traffic hits Rule 1 first, so it is allowed. Swap them, and now Rule 1 denies it — the same two rules give opposite results just by changing the order.
A firewall permits or denies traffic using an ordered ACL, where the first matching rule wins — so rule order decides the outcome. Firewalls belong at every internet gateway and segment boundary. Stateful firewalls track connections; stateless ones only read headers.