Protecting Applications and Data: Managerial Controls and Access Controls
導入済み| English | 意味 |
|---|---|
| at rest/æt rest/ | 静止データ |
| in transit/ɪn ˈtrænsɪt/ | 転送中データ |
| in use/ɪn juːs/ | 使用中データ |
| PII/ˌpiː aɪ ˈaɪ/ | 個人識別情報 (PII) |
| PHI/ˌpiː eɪtʃ ˈaɪ/ | 保護対象健康情報 (PHI) |
| PCI/ˌpiː siː ˈaɪ/ | 支払カード情報 (PCI) |
| RBAC/ˈɑːbæk/ | ロールベースアクセスコントロール (RBAC) |
| RuBAC/ruː bæk/ | ルールベースアクセスコントロール (RuBAC) |
| DAC/ˌdiː eɪ ˈsiː/ | 自律型アクセスコントロール (DAC) |
| MAC/mæk/ | 強制アクセスコントロール (MAC) |
| principle of least privilege/ˈprɪnsɪpl ɒv liːst ˈprɪvɪlɪdʒ/ | 最小権限の原則 |
Data states and laws
- Data can be at rest 静态数据, in transit 传输中数据, or in use 使用中数据.
- Laws protect PII 个人身份信息, PHI 受保护健康信息, and PCI 支付卡信息.
- Sensitive data earns stronger controls.
Four access-control models
- RBAC 基于角色的访问控制: access follows your role.
- RuBAC 基于规则的访问控制: access follows a condition (like time).
- DAC 自主访问控制: the owner decides. MAC 强制访问控制: a central admin sets levels.
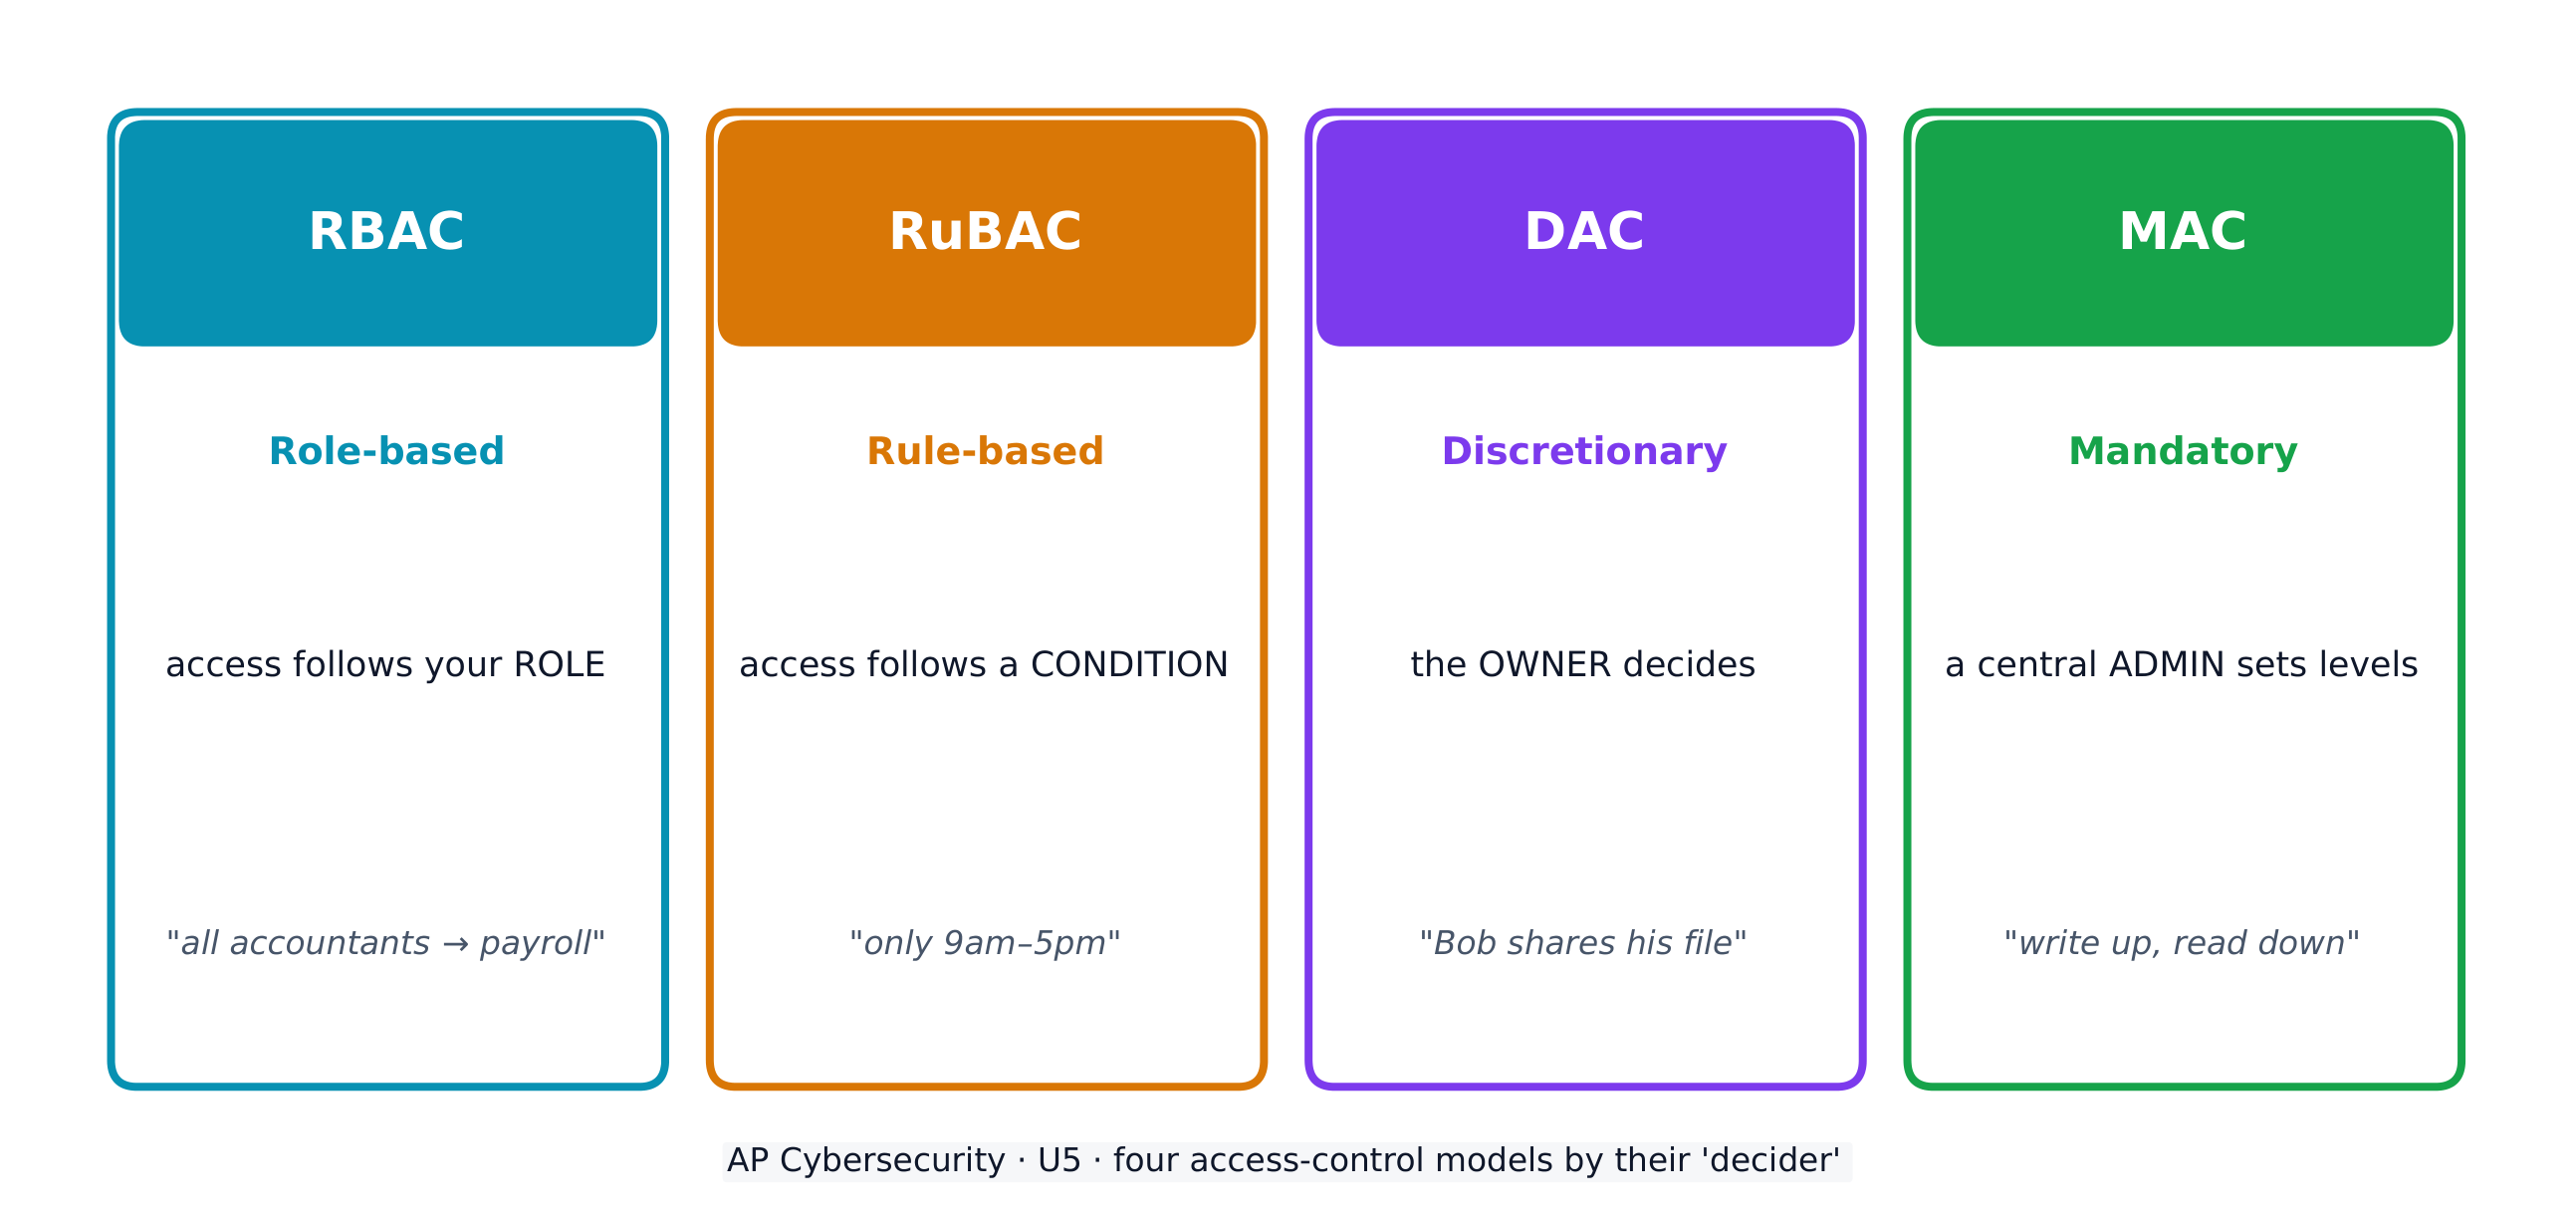
Four access-control models, by who decides access
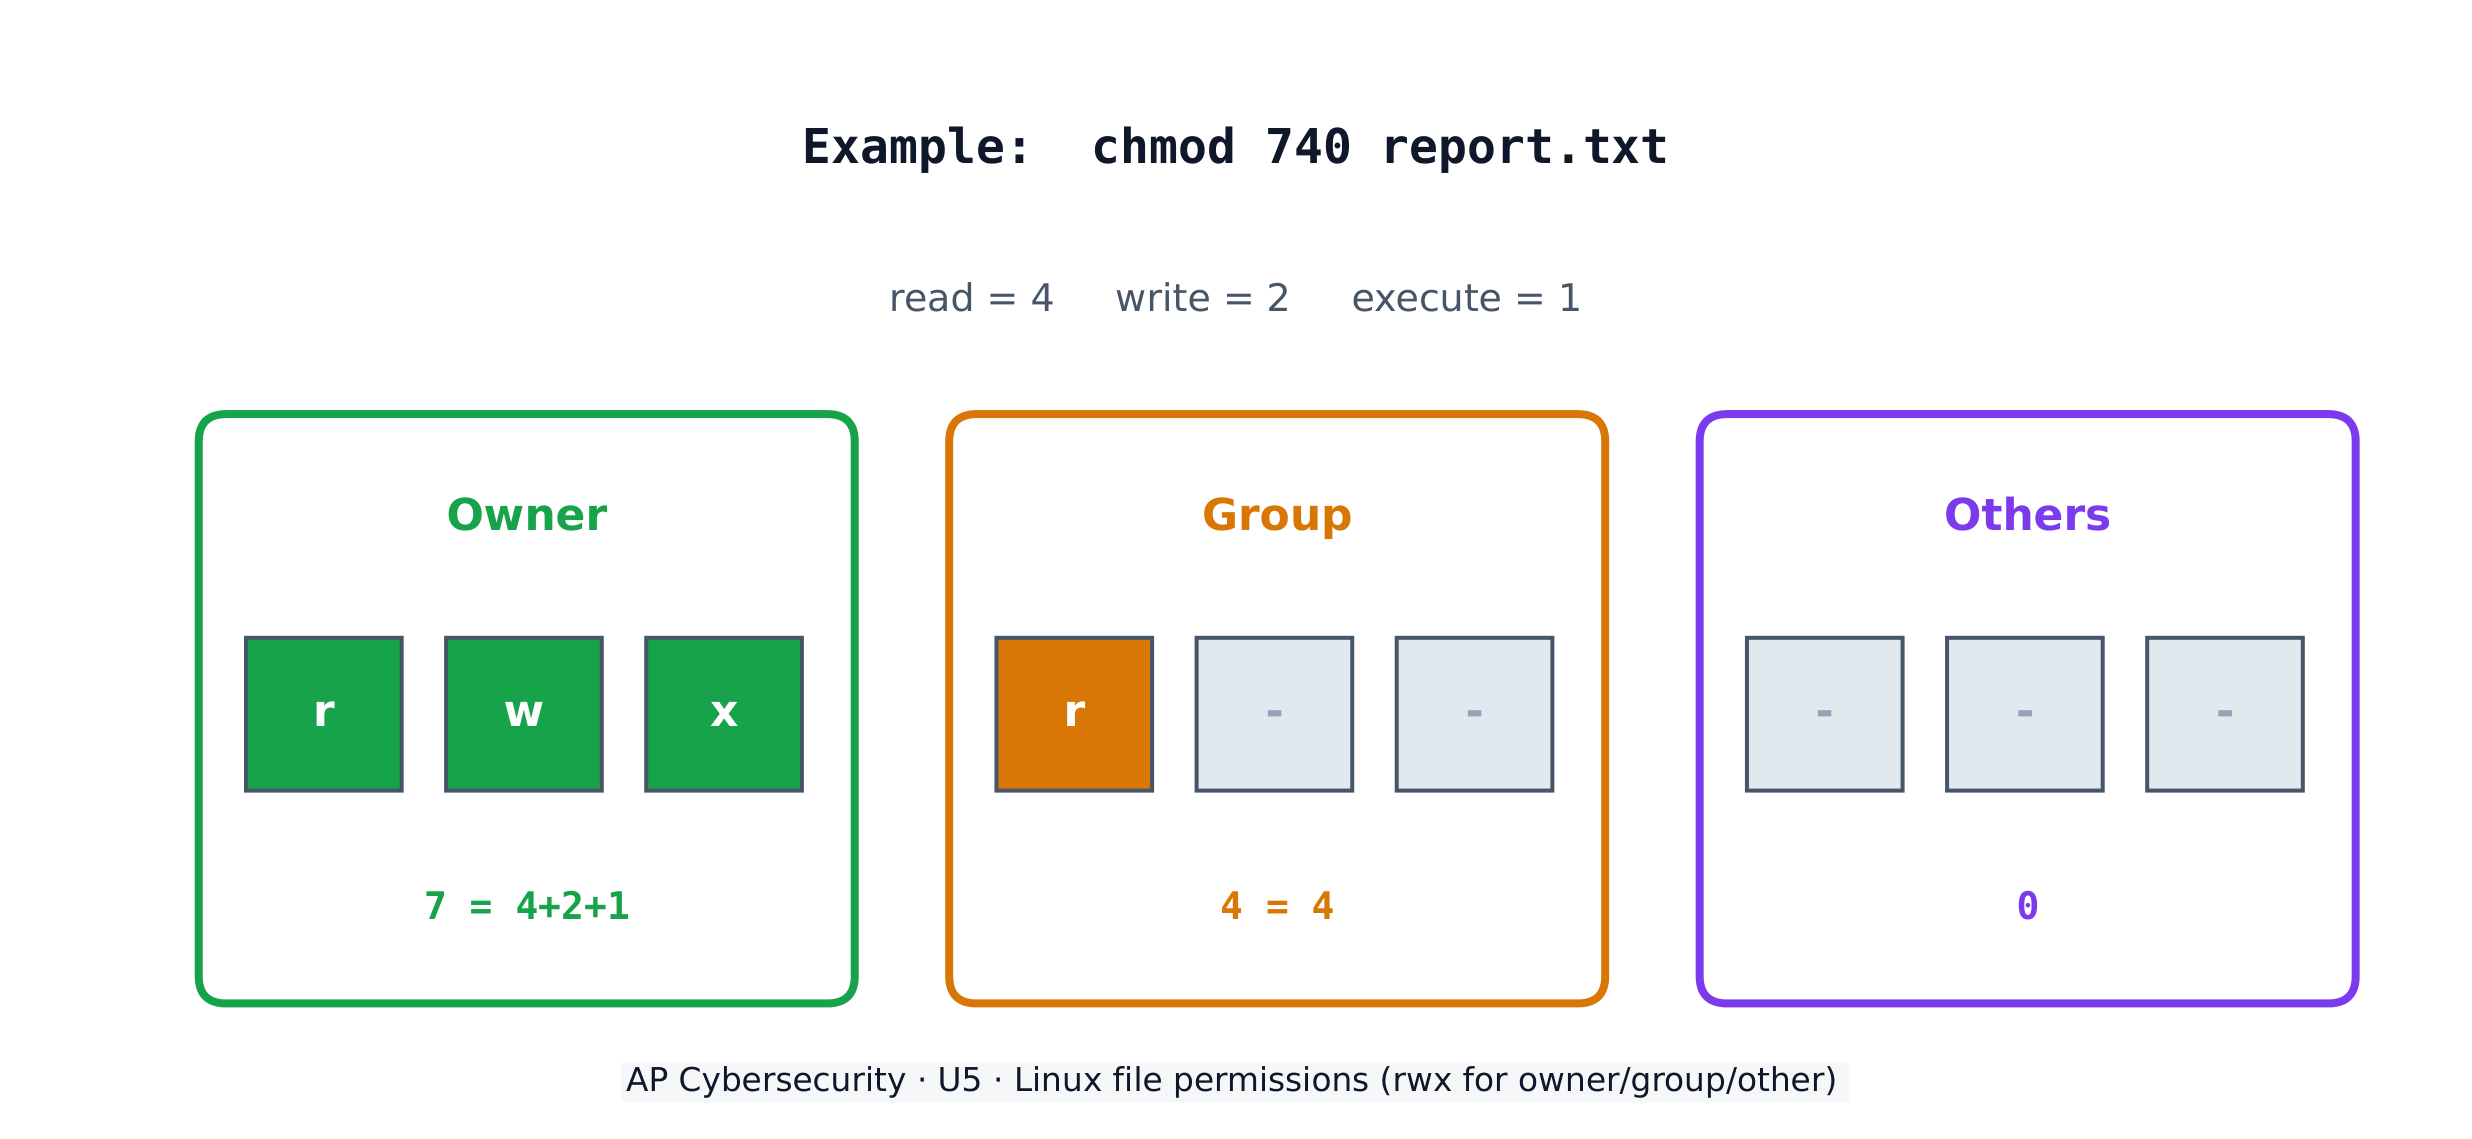
Linux file permissions: read, write and execute for owner, group and others
Which access-control model fits the rule?
RBAC follows your role; RuBAC follows a condition; DAC lets the owner decide; MAC uses central levels.
"Allow access only during business hours" describes which model?
難易度 1/5 · 100 コイン + 今日初回完了時に小ボーナス付与
A condition (time) = RuBAC.
In ____ access control, the owner of a file decides who else may use it.
難易度 1/5 · 100 コイン + 今日初回完了時に小ボーナス付与
DAC = the owner decides.
Linux permissions
- Each file has read (4), write (2), execute (1) for owner, group, others.
chmod 640= owner read+write (6), group read (4), others none (0).- The principle of least privilege 最小权限原则 guides every model.
Tell the four access models apart by their decider, not their name. RBAC = your role, RuBAC = a condition, DAC = the file's owner, MAC = a central admin. Exam questions describe the rule and ask you to name the model.
What single number sets owner read+write, group read, others none? (chmod ___)
難易度 2/5 · 140 コイン + 今日初回完了時に小ボーナス付与
6 (4+2), 4, 0 → 640.
The principle of least privilege gives each user full access so work is never blocked.
難易度 1/5 · 100 コイン + 今日初回完了時に小ボーナス付与
False. Least privilege gives each entity exactly the access it needs and no more, limiting the damage if an account is compromised.
Match each access model to its decider.
難易度 2/5 · 140 コイン + 今日初回完了時に小ボーナス付与
Each model has a different decider.
To set report.txt so the owner can read and write, the group can only read, and others get nothing: read+write = 4+2 = 6, read = 4, none = 0. The command is chmod 640 report.txt.
Data is protected by its state and by law (PII/PHI/PCI). Access control uses four models — RBAC (role), RuBAC (condition), DAC (owner), MAC (admin levels) — all guided by least privilege. On Linux, permissions add read 4 + write 2 + execute 1 per group.